Hello & Welcome
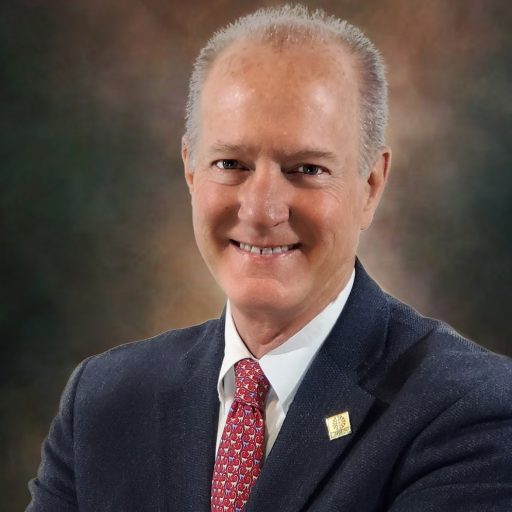
I’M Darrell Bateman
STRATEGIC CYBERSECURITY & RISK ADVISOR | BOARD MEMBER
Seasoned executive leader with extensive experience developing and executing cybersecurity, information technology, and risk management strategies in highly regulated environments. Proven success establishing and maturing enterprise security programs, guiding organizations through digital transformation, and aligning information security initiatives with business objectives. Recognized for board-level communication, regulatory expertise, and leadership in driving operational resilience and compliance excellence. Trusted advisor to financial institutions, higher education, and technology innovators.
Darrell Bateman
TOP SKILLS
CYBERSECURITY STRATEGY & GOVERNANCE
REGULATORY COMPLIANCE
INFORMATION SECURITY RISK MANAGEMENT
THIRD-PARTY & VENDOR RISK OVERSIGHT
CLOUD SECURITY & COMPLIANCE
BUSINESS CONTINUITY & INCIDENT RESPONSE
BOARD & EXECUTIVE COMMUNICATION
SECURITY PROGRAM DEVELOPMENT & MATURITY
PROJECT & PROGRAM MANAGEMENT
AUDIT & EXAMINER RELATIONS
MERGERS, ACQUISITIONS & INTEGRATIONS RISK
PUBLIC SECTOR & HIGHER EDUCATION SECURITY LEADERSHIP
PROVEN TRACK RECORD IN
Cybersecurity Leadership & Governance
- Built and led comprehensive cybersecurity programs aligned with federal and state regulatory frameworks for financial and higher education institutions.
- Established the Chief Information Security Office and governance structures for a $4B regional bank, achieving top regulatory ratings.
- Developed and implemented security policies, frameworks, and performance metrics based on NIST and FFIEC guidance.
- Delivered board and executive briefings translating complex security risk into actionable strategic insight.
- Directed cross-functional teams integrating IT, operations, and risk to strengthen enterprise security posture.
Regulatory Compliance & Risk Management
- Extensive experience with GLBA, HIPAA, PCI DSS, SOC (SSAE16/18), and FERPA compliance programs.
- Designed and executed enterprise risk assessments and internal controls aligned with examiner expectations.
- Led successful federal and state audits resulting in exemplary compliance ratings.
- Coordinated pandemic and incident response programs ensuring business continuity and operational resilience.
- Oversaw due diligence, risk assessment, and contract negotiations for critical vendors and service providers.
Board, Advisory, and Strategic Influence
- Regularly presents to public company and university boards on cybersecurity strategy, regulatory trends, and risk posture.
- Appointed to Texas state advisory committee defining cybersecurity requirements for higher education.
- Active board member for technology start-ups and innovation councils, providing strategic guidance on growth and security alignment.
- Serves as a subject matter expert for (ISC)² in developing CISSP certification content.
- Recognized as a Distinguished Engineer and thought leader driving collaboration between academia, industry, and government.